活动预告|CodeWisdom可信AI系统系列学术报告第14期:可信大语言模型智能体
CodeWisdom 2026-08-16 13:56 吉林
活动时间:2026年8月18日(周二)10:30
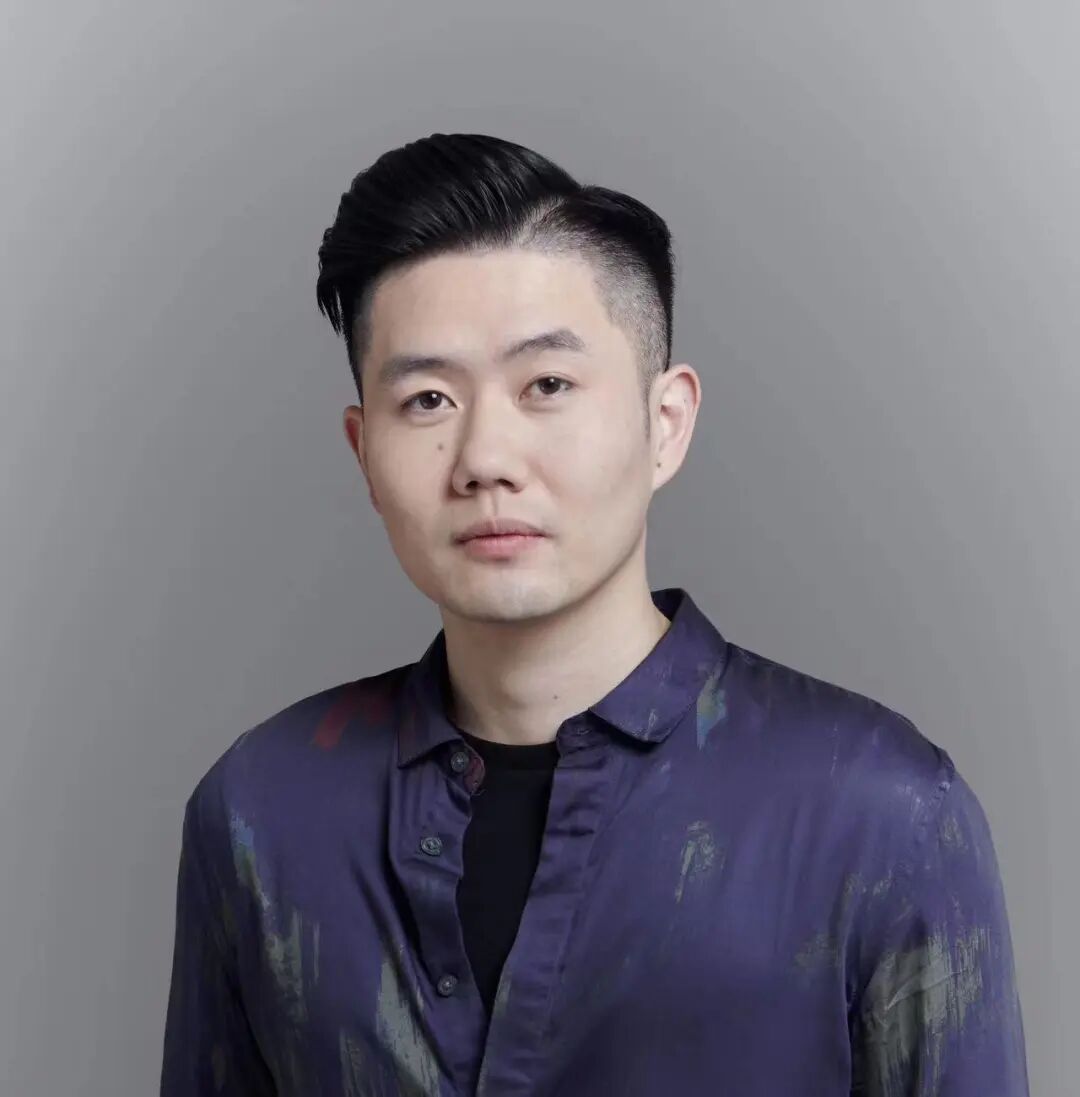
Dongdong She
Assistant professor at the Hong Kong University of Science and Technology, CSE department
Summary
Title
Trustworthy LLM Agents: Uncovering and Securing the Attack Surface from a Systems Perspective
Abstract
The rapid evolution of LLM foundation models and agents is reshaping daily life—from general-purpose AI assistants such as ChatGPT to specialized coding agents and autonomous deep-research agents. Yet this leap in capability introduces a new class of security and privacy challenges that traditional defenses were never designed to handle. Ensuring trustworthiness in LLM agents has thus become a fundamental and urgent problem for both academia and industry.
In this talk, I will present a systematic security framework for trustworthy LLM agents, organized around three critical and previously under-examined system modules that every production agent relies upon: (1) Prompt Compression, where we show that widely adopted compression modules (e.g., LLMLingua) expose a new attack surface that causes an adversarial information loss to manipulate LLM agent behavior; (2) Semantic Caching, where we reveal an inherent security vs. performance trade-off in the semantic cache design and demonstrate practical cache collision attacks that can hijack LLM responses and agent actions; and (3) Agentic Tool Invocation, where we show that a novel mode-behavior gap in the tool-invocation pipeline of major real-world coding agents(Cursor, Claude Code) can be exploited into security-sensitive system prompt leakage and a further Remote Code Execution(RCE). We also demonstrate the first query-agnostic indirect prompt injection that fires under arbitrary user queries.
Speaker
Dongdong She is an Assistant Professor in the Department of Computer Science and Engineering at the Hong Kong University of Science and Technology (HKUST). He received his Ph.D. from the Department of Computer Science at Columbia University, his M.S. from UC Riverside, and his B.S. from Huazhong University of Science and Technology. His research lies at the intersection of security and machine learning, with a current focus on the security of LLM-powered agents and on leveraging LLMs to solve traditional security problems such as program analysis and vulnerability discovery. His work has been recognized with multiple prestigious awards at top-tier venues, including the IEEE S&P Distinguished Paper Award, the ISSTA Distinguished Paper Award, the ACM CCS Best Paper Runner-Up Award, and the NYU CSAW Applied Research Finalist Award. He has published extensively at premier security and software engineering conferences, including IEEE S&P, CCS, USENIX Security, FSE, ISSTA, and OOPSLA.
Schedule
❖
时间:
2026年8月18日(周二)10:30
❖
腾讯会议:
会议号:797 887 323
密码:386190
❖
地点:
复旦大学江湾校区二号交叉学科楼A2003